Whitelist
DeepFilter puts every incoming email through a long series of security checks and gathers the threat signals it collects into a single score; when the score passes the threshold, the email is quarantined or rejected. From time to time these checks find a legitimate sender suspicious by mistake — emails from a business partner you correspond with regularly may keep landing in quarantine. This is called a false positive.
The Whitelist lets you define sender addresses or domains you trust and exempt their emails from the checks you choose. That keeps emails from your known business partners, suppliers and corporate services from being blocked by mistake. You can grant the exemption per check (skip only the check that causes trouble) or give a sender Full Pass, which turns off every check at once.
You use this screen when a trusted sender's emails are repeatedly flagged as spam, or when you want to establish trust for a particular domain in advance.
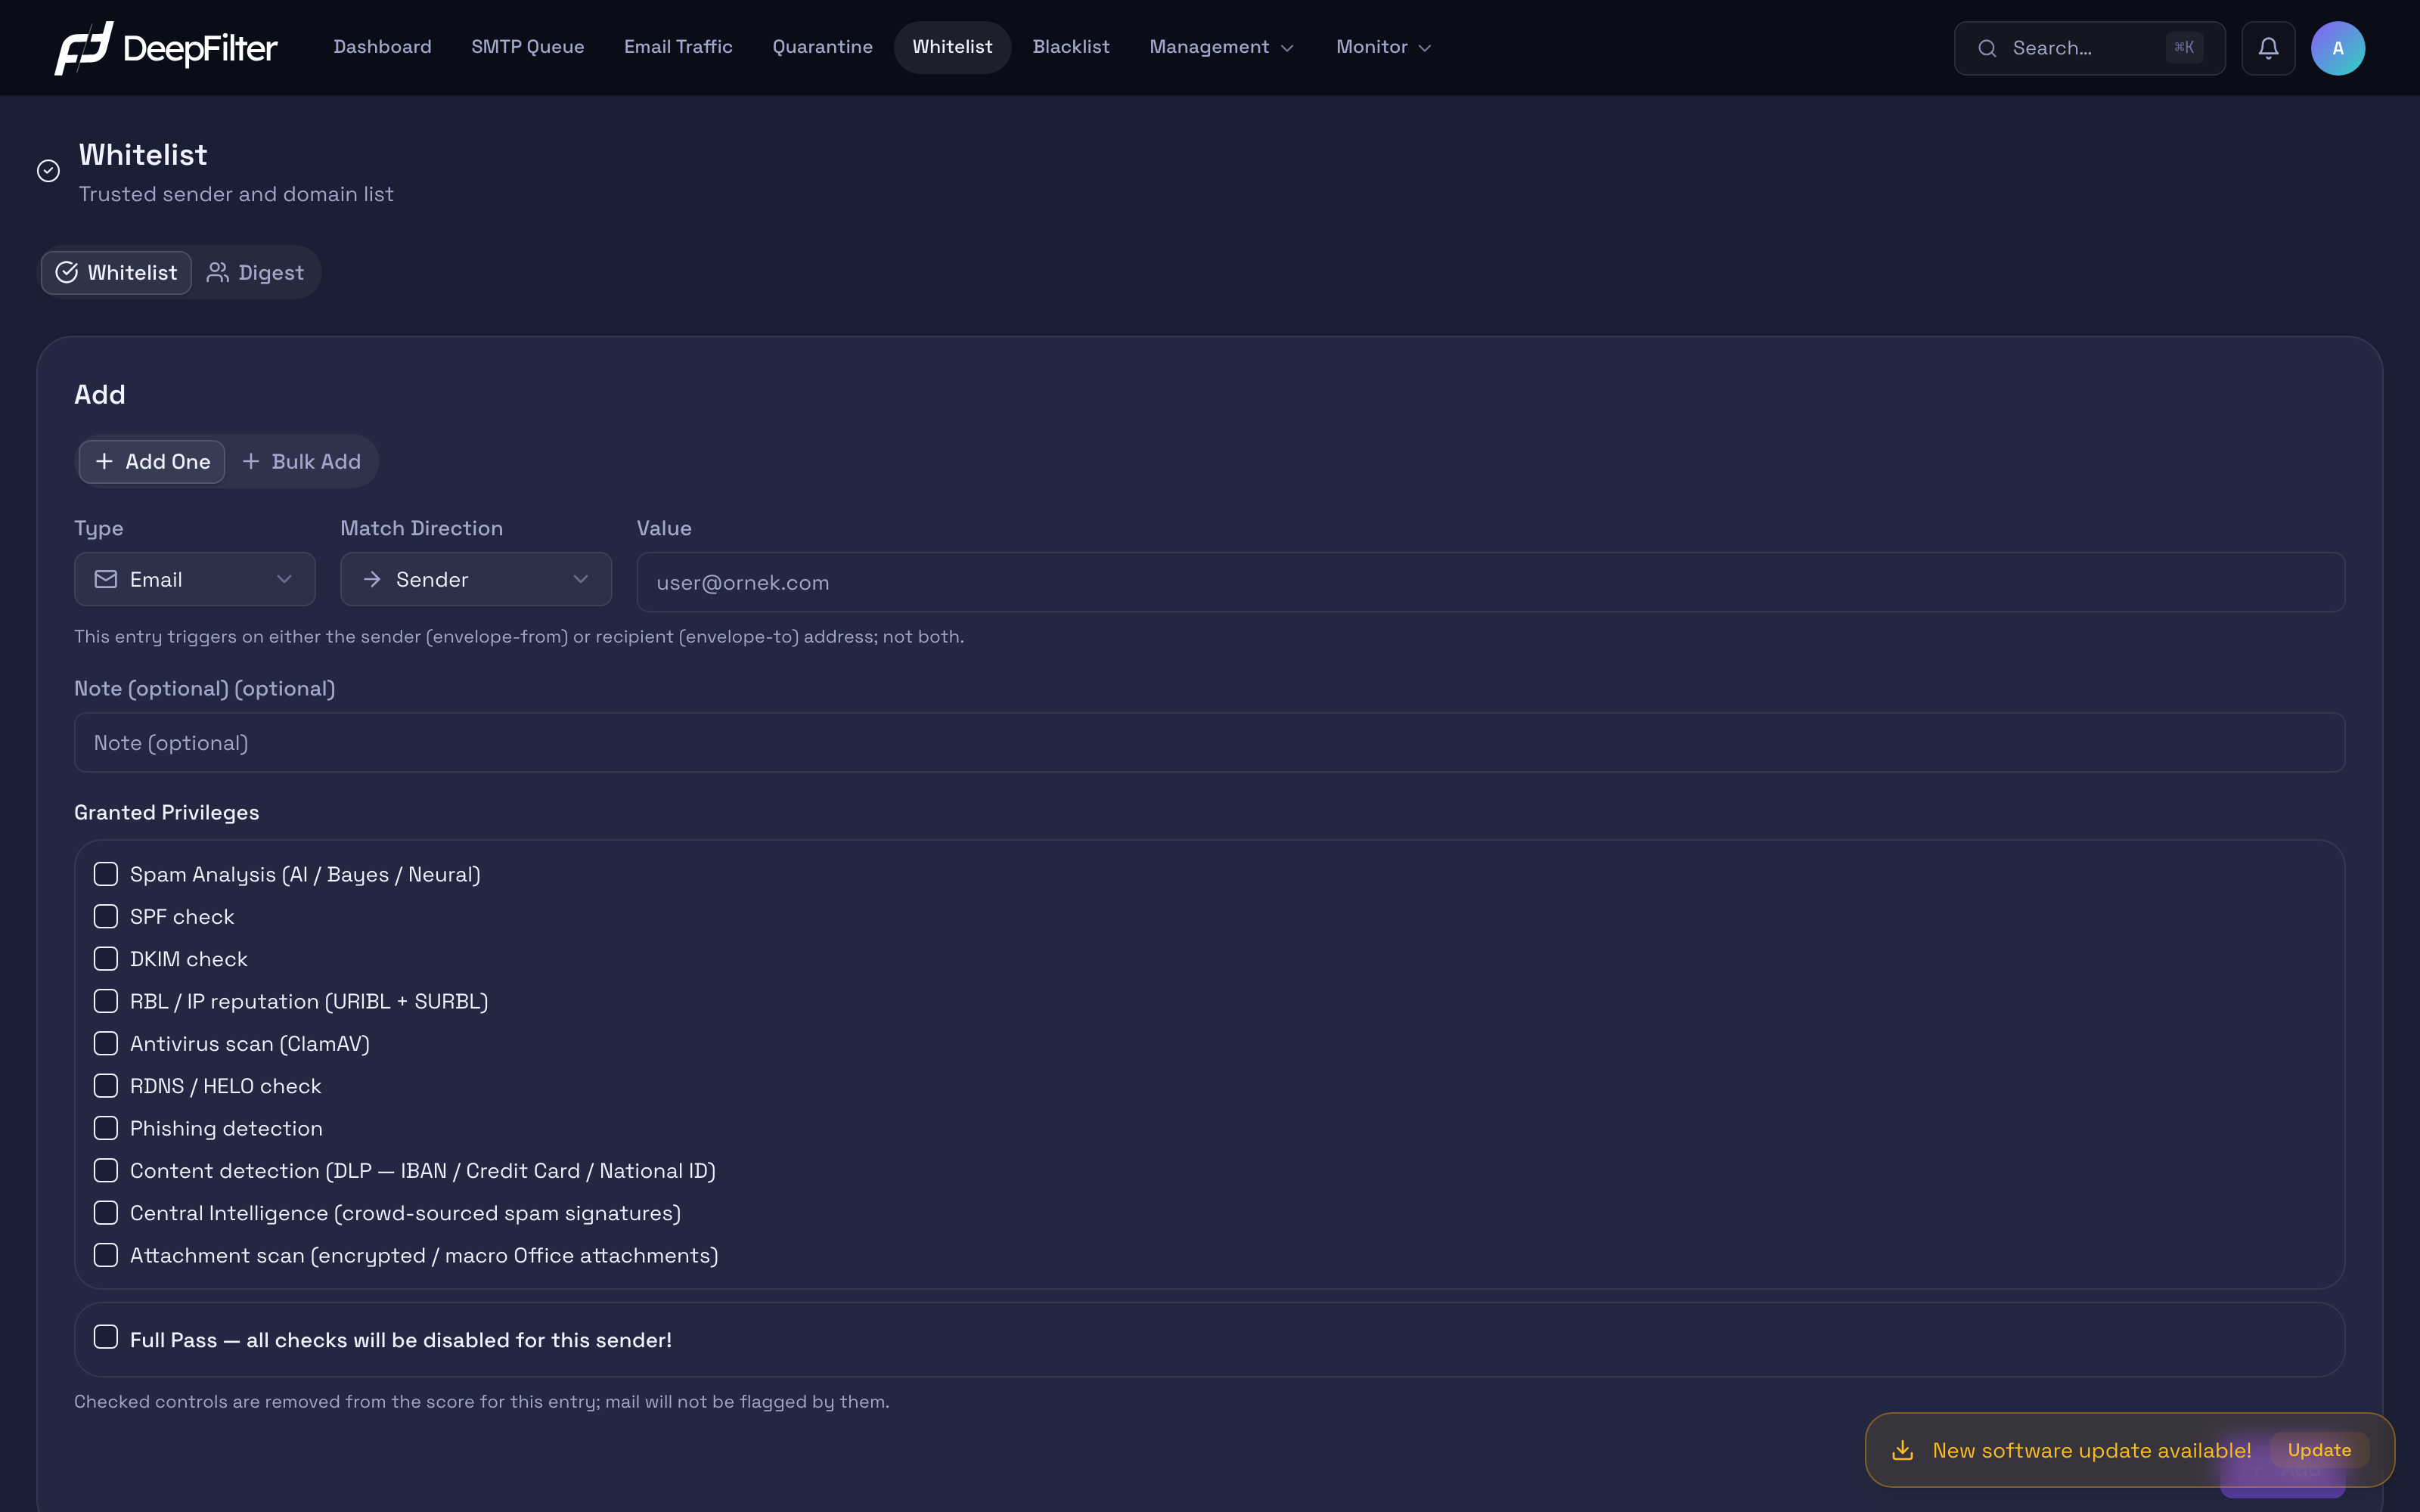
The Whitelist and Digest tabs at the top of the screen split the page in two: the first manages the trust entries, the second presents a summary of the users' own allow lists.
Settings
A new entry is created in the Add section. This section offers two modes: Add One (a single entry) and Bulk Add (a multi-line list). The fields below belong to Add One mode.
Type — decides whether the entry covers a single email address or an entire domain. (default: Email)
- Email — only the exact address you enter is exempt (e.g.
user@ornek.com). - Domain — every address belonging to that domain is exempt (e.g.
ornek.com→ everyone on that domain).
Sometimes you need to trust a single correspondent, sometimes a whole organization; this field separates the two scopes. Choosing Domain spreads the exemption across an entire organization: convenient, but it also widens your attack surface, because anyone impersonating that domain becomes exempt too. The narrowest and safest scope is a single Email address. IP addresses cannot be added to the whitelist; IP-based exceptions are managed in the Blacklist and Firewall modules.
Match Direction — decides whether the entry triggers on the sender address or the recipient address. (default: Sender)
- Sender — the exemption applies when the email's envelope sender address (envelope-from) matches this entry.
- Recipient — the exemption applies when the email's envelope recipient address (envelope-to) matches this entry.
Sometimes you want to trust a particular sender, sometimes a particular recipient (for example everything arriving at a critical corporate mailbox). A single entry never looks at both the sender and the recipient; you pick one of the two. If you want the same value exempt in both directions, you create two separate entries.
Value — the email address or domain to exempt. The placeholder text in the field
changes with the Type you selected (user@ornek.com or ornek.com). Leading and trailing
whitespace is stripped from what you enter, the text is lowercased and its format is
validated; an invalid address or domain is not saved.
Note (optional) — free text explaining why the entry was added. A whitelist grows over time; noting which entry was added for whom, when and why makes auditing and cleanup much easier later on.
Granted Privileges
Granted Privileges — ten exemption checkboxes where you pick, one by one, which security checks are skipped when this entry matches. (default: none checked)
Every check you tick is removed from the score calculation for this sender's emails; that check can no longer catch the email. The checks you leave unticked keep working normally. Usually you only have trouble with a single check for a given sender (for example its server is on a blocklist, so it trips IP reputation). Skipping just that check and leaving all other protection standing is far safer than a blanket exemption.
The more boxes you tick, the less the sender is inspected: false positives drop, but so does the effort required by an attacker impersonating that address. Start with as few boxes as possible.
| Control (label on screen) | What is skipped if you check it |
|---|---|
| Spam Analysis (AI / Bayes / Neural) | Artificial intelligence and statistical spam classification |
| SPF check | SPF verification of the sender domain |
| DKIM check | DKIM signature verification |
| RBL / IP reputation (URIBL + SURBL) | Sender IP and connection reputation checks |
| Antivirus scan (ClamAV) | Malware / virus scanning |
| Attachment scan | Structural attachment analysis (encrypted or macro-bearing Office attachments, links hidden inside attachments) |
| RDNS / HELO check | Reverse DNS and HELO consistency check |
| Phishing detection | Phishing signals |
| Content detection (DLP — IBAN / Credit Card / National ID) | Sensitive data (IBAN, credit card, national ID) content rules |
| Central Intelligence | Known threat fingerprints collected across the DeepFilter network |
If you tick no boxes at all, the entry applies no exemption on its own: the email goes through every check normally and its score does not drop; the entry is merely written to the processing log as a "known sender". For the exemption to have a real effect, at least one check (or Full Pass) must be ticked.
Exempting the SPF and DKIM checks calls for particular care: these are exactly the verifications that catch sender spoofing attempts. If you exempt a sender from these two checks, an authentication failure from an attacker impersonating that address is no longer caught either. Tick these boxes only when you genuinely have to.
Some definite-threat signals are not skipped by a granular exemption even if you tick the relevant box: confirmed phishing patterns, dangerous extensions inside archives (compressed files) and the sensitive-data extension defense always stay active. This protection is deliberate; the only way to bypass these signals as well is Full Pass, and that carries every risk described below.
Full Pass
Full Pass — the master exemption switch that, when ticked, turns off every security check at once for this sender (or recipient). (default: off)
When it is ticked, the ten granular boxes are disabled and the entry is marked so that the email's score is driven far below the threshold in every scenario. In practice no email from this sender trips any check. For fully trusted sources such as your own internal systems, granting blanket trust can be more practical than picking checks one at a time.
Full Pass is the most powerful and the most dangerous option: turning it on ends false positives entirely, but it effectively switches the filter off for that address or domain. Leaving it off and selecting only the granular boxes you need is safer in almost every situation.
When you tick Full Pass, a red warning appears on the screen. Granting this box to a domain (Type: Domain) is the riskiest combination; keep the scope narrow by using it for individual email addresses wherever possible. The security risk created by a broadly scoped Full Pass is covered in detail in the Points to Watch section.
Adding an Entry to the Whitelist
Prerequisites
- Confirm that the emails from the sender you are adding really are legitimate; granting trust to a spoofed address lets spam or malicious email bypass the filter.
- If you hold the domain admin role, you can only add entries for the domains you are authorized for.
Steps
- Open the Whitelist screen and make sure Add One mode is selected in the Add section.
- Choose Email or Domain in the Type field.
- Choose Sender or Recipient in the Match Direction field.
- Enter the address or domain you trust in the Value field
(e.g.
accounting@ornek.comorornek.com). - Optionally write the reason for the entry in the Note field.
- Under Granted Privileges, tick only the checks that cause trouble. If you are unsure, start with the narrowest selection; you can widen the exemption later.
- Click the Add button at the bottom right.
Verification — how to know it worked
- The entry appears in the list. When a test email arrives from this sender, the processing log shows that the check you exempted was not added to the score and that the email was delivered instead of quarantined.
To add several entries at once, switch to Bulk Add mode. In this mode you do not pick a
Type; every line is detected automatically: a line containing @ counts as an email
address, a line without one as a domain. Lines starting with # and blank lines are
skipped (you can use them as comments or separators inside the list); duplicate and invalid
lines are dropped. Before the list is saved, a preview shows you how many entries will be
added.
Deleting an Entry
Steps
- Find the entry you want to remove in the Whitelist list.
- Remove it from the list with the delete action on the entry's row.
Verification — how to know it worked
- The entry disappears from the list. From that moment on the exemption defined for that sender ends; the next email goes through every check normally. Deleting an entry causes no data loss; you can add the same address again whenever you need to.
The Digest Tab
The Digest tab at the top of the screen presents an administrator summary of the addresses end users have added to their own personal allow lists (per-recipient allow). From here you see, in one place, which user allowed which sender.
Per-recipient allow is deliberately narrower than the whitelist on this page. The Whitelist is defined by an administrator, can reach domain scope and offers ten granular controls plus Full Pass. A per-recipient allow is defined by the end user themselves and can only skip content- and reputation-type checks (spam analysis, IP reputation, antivirus, phishing, sensitive data content); it does not cover authentication checks such as SPF, DKIM and RDNS/HELO, nor Full Pass. So even if an address a user allowed is spoofed, the authentication failure is still caught and the email stays in quarantine.
The Digest tab is visible only to the full administrator; it is hidden for the domain admin role.
Points to Watch
The whitelist works by looking at the sender/recipient addresses in the email's envelope and headers. Those addresses can technically be forged: an attacker can write an address you consider "trusted" as the sender of their own email. The broader the exemption you define (a domain rather than a single address; Full Pass rather than a single granular control), the wider the door that forgery opens for you.
The safest approach is always to start with the narrowest definition: a single email address and only the single check that causes trouble. If the problem persists, widen the scope step by step. Domain scope and Full Pass are a last resort, for when nothing else is left and you trust the source absolutely.
Granting Full Pass to a domain is the riskiest combination: everyone impersonating that domain becomes exempt from every security check, and malicious email reaches the user directly. Use Full Pass only for individual email addresses whose source you trust absolutely; avoid granting it to an entire domain.
Troubleshooting
I added it to the whitelist but the email is still in quarantine
- If you ticked no checks on the entry, no exemption is applied. Tick at least one check or Full Pass.
- Compare the entry's Match Direction with the direction of the email. Use Sender to trust an external sender, and Recipient for everything arriving at a mailbox you want to protect.
- The email may have tripped a definite-threat signal that a granular exemption cannot skip (confirmed phishing, a dangerous extension inside an archive, a sensitive-data extension). Only Full Pass skips these signals.
I ticked a check but the score did not change
- Verify the direction match described above first.
- The new entry may not have reached the filtering engine yet; the change syncs shortly.
The entry cannot be added, or an "Add a domain first" warning appears
- If you hold the domain admin role, you can only add entries for the domains you are authorized for. If you are not authorized for any domain, a domain must be defined first.
The value is not accepted
- The format of the text you entered may be invalid. An email address must look like
user@ornek.comand a domain likeornek.com.